Enroll with a Token2 Programmable Token
Program a Token2 programmable token with the Token2 NFC Burner 2 app, then sign in with the 6-digit code it displays.
A Token2 programmable token is a hardware token that displays one-time codes (TOTP). You program it once, from the QR code UserLock displays at enrollment, with an Android phone and the Token2 NFC Burner 2 app. At sign-in, you enter the code displayed on the token.
An Android phone with NFC turned on and the Token2 NFC Burner 2 app, version 2.1 or later. The same phone can program tokens for several users, for example an administrator’s phone.
Your domain credentials.
If you already use another MFA method, ask your administrator to reset your MFA configuration first.
A Windows version of the NFC Burner app is also available. This guide uses the Android app.
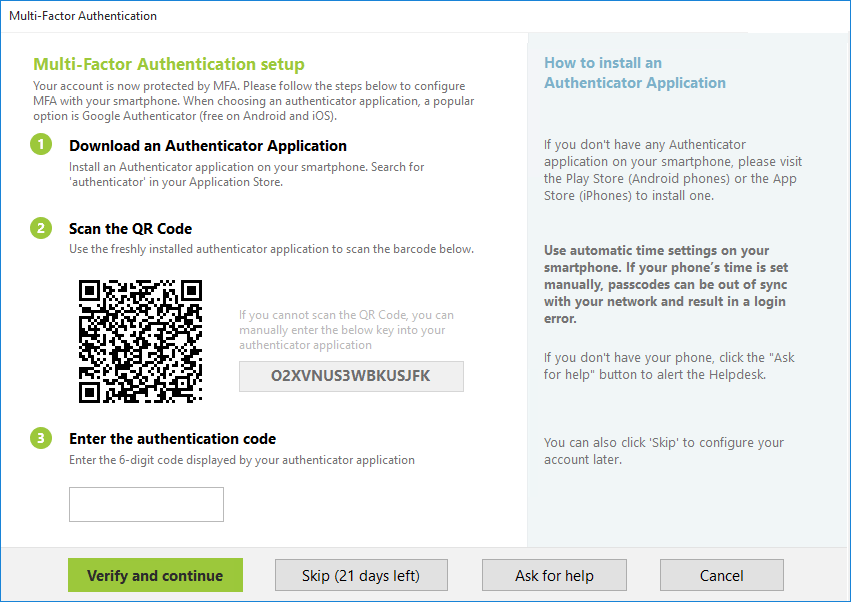
Sign in with your Windows credentials. If UserLock asks you to choose a method, select Authenticator App. A QR code appears.
On the Android phone, open Token2 NFC Burner 2 and tap Scan QR.
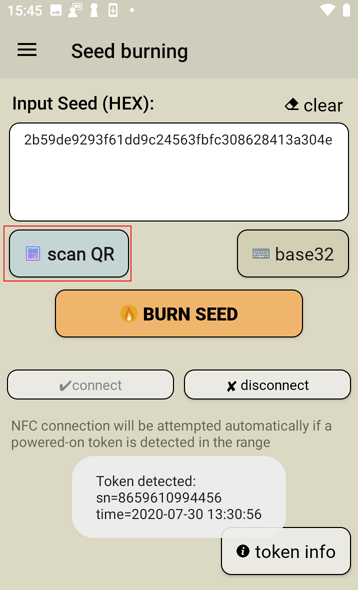
Point the camera at the QR code. The camera closes when the scan succeeds. If you can’t scan the code, tap Base32 and enter the key displayed with the QR code.
Turn on the token and place it on the phone’s NFC antenna.
Tap Connect.
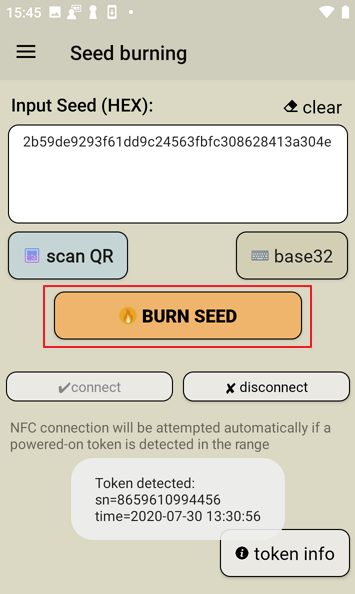
Tap BURN SEED. The app shows Burning…, then Burn seed successful.
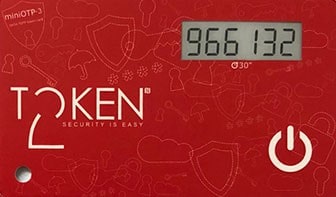
Turn the token off, then on again.
If UserLock asks you to set up an additional method, follow the on-screen instructions. If you can’t, contact your administrator.
If the connection fails, check that NFC is turned on, move the token slightly to align it with the antenna, and check that the token is on. See also Troubleshooting NFC link stability in the Token2 documentation.
In the UserLock enrollment dialog, enter the 6-digit code displayed on the token.
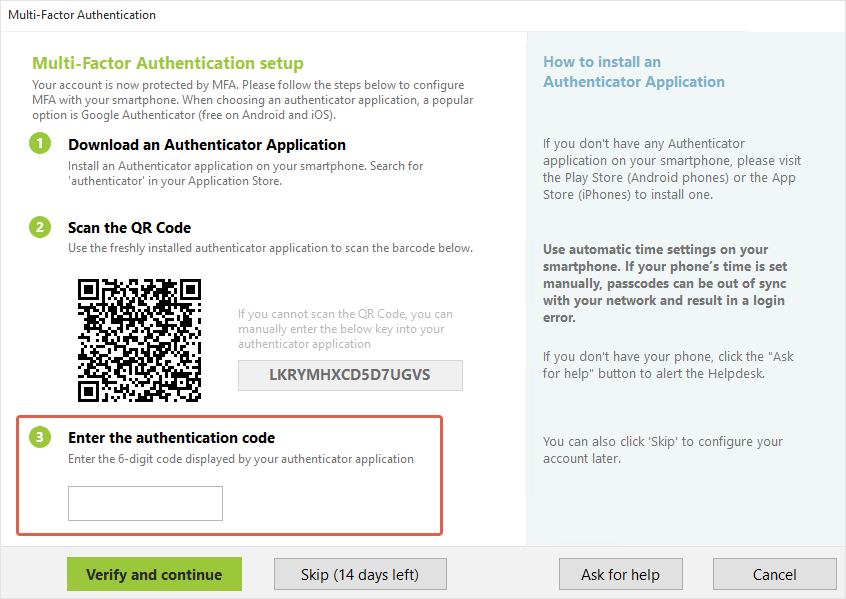
Click Verify and continue.
The token is now paired with your account. At your next sign-ins, enter your Windows credentials, then the code displayed on the token.
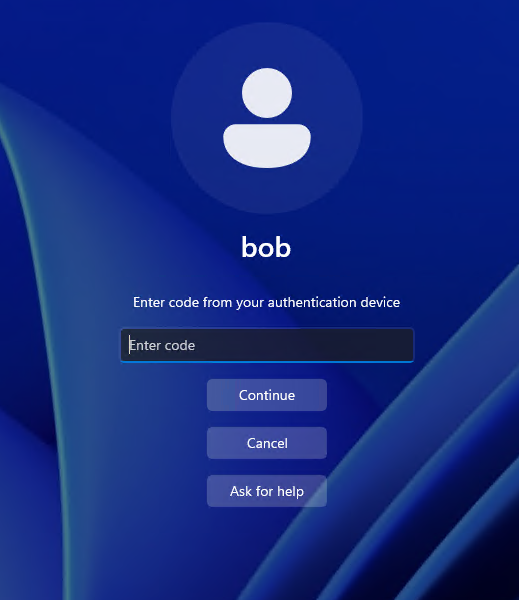
If you lose your token, contact your administrator. If you saved recovery codes, use one to sign in in the meantime.
Contact your administrator, who resets your MFA configuration. You then enroll again at your next sign-in.
If you enrolled an additional method or saved recovery codes, use them to sign in in the meantime.